Autonomous software governance and AI security

IT Professional Weekly Overview — Week of September 7–September 12, 2026

This week’s IT highlights focused on the challenges of managing autonomous software in production. Key themes included evolving security practices, agent governance, and the shift in engineering roles. The discussions emphasize the need for robust boundary designs and integration strategies to address risks associated with AI’s rapid development and implementation.

Continue reading

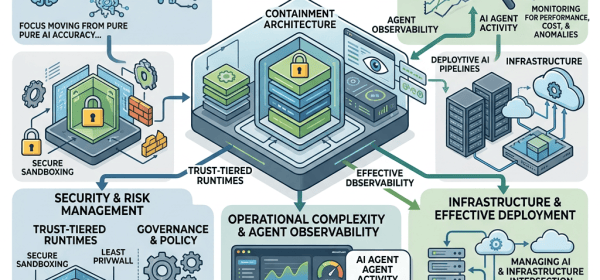
Infographic showing enterprise AI containment, governance, security, observability, and infrastructure architecture

IT Professional Weekly Wrap-Up — Week of September 7–September 12, 2026

This week’s roundup highlights a shift in enterprise AI discussions from model capabilities to containment architecture. Key themes include security concerns, operational complexities, and governance in relation to AI agents. As organizations adapt, they must focus on trust-tiered runtimes, agent observability, and managing the intersection of AI and infrastructure for effective deployment.

Continue reading

How Microsoft’s Physical Security Engineering Team scaled hybrid operations with Azure Arc and Azure Virtual Desktop

How Microsoft’s Physical Security Engineering Team scaled hybrid operations with Azure Arc and Azure Virtual Desktop

This case is less about cloud migration than about standardising hybrid operations at scale. For IT teams, the value lies in how central governance, image-based maintenance, user-session telemetry, and tighter identity controls can improve resilience and consistency without moving locally dependent workloads.

Continue reading

Software engineers' new job isn't writing code — it's designing the boundaries AI agents can't break

Software engineers’ new job isn’t writing code — it’s designing the boundaries AI agents can’t break

As AI agents take over more code generation, the engineering challenge shifts to enforceable boundaries: contracts, policy controls, testable semantics, and least-privilege automation. The real differentiator for IT teams is whether their architecture can turn agent output into safe, auditable, business-correct change.

Continue reading

MCP went stateless: Is your AWS MCP server deployment well-architected?

MCP went stateless: Is your AWS MCP server deployment well-architected?

MCP’s stateless core can simplify AWS deployments, but the real work shifts into tool and platform design: explicit state identifiers, replay-safe operations, ownership enforcement, version-aware migration, and gateway controls all become critical if teams want the scaling and cost benefits without new reliability or security gaps.

Continue reading

1 2 3 4 5 6 … 186