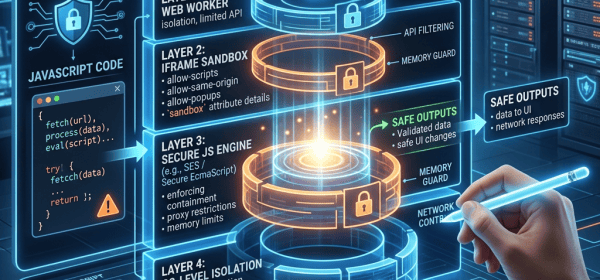
The isolated-vm flaw is a reminder that secure code execution depends on more than the sandbox primitive itself. For IT teams running user- or AI-generated JavaScript, the real risk lies in host-guest bindings, serialization paths and whether process-level isolation exists beyond the Node.js runtime.