

The practical decision is less about choosing Docker Hub or a private registry than deciding where trust is established in the container supply chain. A registry should be treated as an enforcement point, not just a storage endpoint. If teams mirror public images internally but do not attach provenance checks, vulnerability gates and change controls, they have only relocated the risk.
For platform and DevOps teams, the important design question is how images move from external source to production-approved artifact. A defensible pattern is to separate that flow into stages: ingest approved upstream images, scan and sign them, rebuild or harden where necessary, then promote only immutable digests into internal registries for deployment. That architecture reduces exposure to mutable tags, surprise upstream changes and inconsistent image selection across environments.
There are trade-offs. Private registries improve governance, but they also introduce operational burden around replication, retention, access control, high availability and patching of the registry service itself. Organizations with multiple clusters or regions also need to think about image distribution latency, cache strategy and whether every environment pulls from a central registry or from synchronized local mirrors.
For security teams, policy automation matters more than registry branding. The strongest control set usually includes digest pinning, signature verification in CI/CD and at admission time, base-image allowlists, SBOM generation and routine review of dormant images that still carry exploitable packages. The real maturity signal is not that a company runs a private registry; it is that every deployed image has a verifiable path from source, validation and approval to runtime.
In the race to accelerate software delivery, Docker Hub has become a default starting point for developers and organizations alike. It offers convenience, accessibility, and a vast ecosystem of pre-built images that can jumpstart nearly any project. But as container adoption matures, so does the understanding that convenience comes with tradeoffs, and this is especially true for security. The choice between public and private container registries is a strategic decision that directly impacts an organization’s risk profile.
The Appeal of Public Registries
Public registries like Docker Hub have played a pivotal role in the rise of containerization. They provide a centralized location where developers can publish, discover, and share images across the global community. For teams looking to move quickly, the ability to pull a ready-made image instead of building from scratch is a major advantage.
To understand the appeal, it helps to consider: what is Docker Hub at its core? In summary, it’s a publicly accessible container registry that hosts millions of images, ranging from official distributions of popular software to community-contributed builds. This openness fuels innovation and collaboration, but it also introduces inherent uncertainty.
Not all images in a public Docker registry are created equal. While some are maintained by trusted vendors and verified publishers, others may be outdated, poorly configured, or even intentionally malicious. The challenge lies in distinguishing between them, often with limited visibility into how those images were built or maintained.
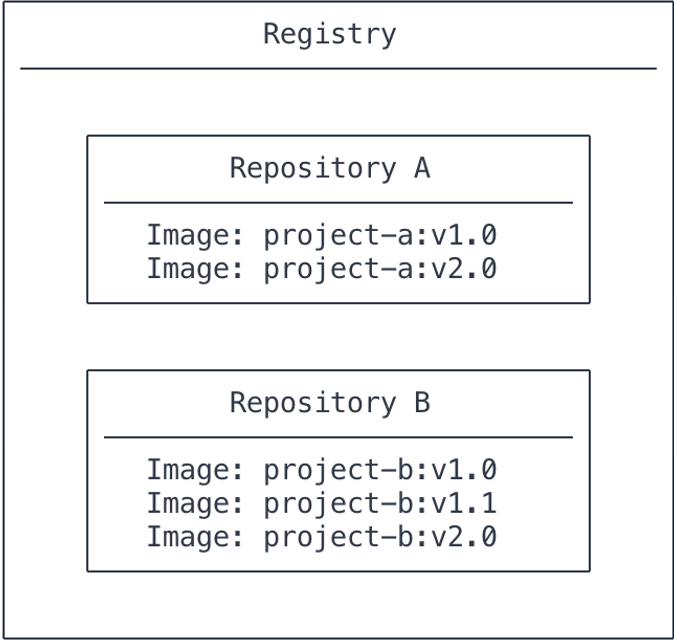
Source: DockerDocs ‘What is a Registry?’
The Hidden Risks of Shared Ecosystems
The open nature of public container registries creates an environment in which trust is frequently assumed rather than verified. Attackers are well aware of this dynamic and increasingly exploit it by uploading images designed to mimic legitimate ones. These images may include subtle modifications, such as embedded malware or backdoors, that are difficult to detect through casual inspection.
Even when images aren’t malicious by design, they can still pose significant risks. Many contain outdated dependencies, unpatched vulnerabilities, or unnecessary packages that expand the attack surface.
Given that images in shared registries often have more dependencies than required, 30% of official images in Docker Hub are recognized as having high-priority vulnerabilities. When organizations pull these images into their environments, they inherit the related risks.
Another concern is the lack of control over the image lifecycle. In Docker Hub or any other public environment, maintainers can update or deprecate images without notice. This creates uncertainty around version consistency and can introduce unexpected changes into deployment pipelines.
These factors highlight a broader issue. Public registries prioritize accessibility and scale, not necessarily security.
The Case for Private Registries
Private registries offer a fundamentally different approach. Instead of relying on a shared ecosystem, organizations maintain their own controlled environments for storing and distributing container images. This shift introduces a higher level of governance and accountability.
A private container registry allows teams to:
- Restrict access to authorized users only
- Enforce security policies and compliance standards
- Maintain visibility into image provenance and dependencies
- Control versioning and lifecycle management
By limiting exposure to external sources, private Docker registries reduce the likelihood of introducing compromised or unverified images into production environments.
As with convenience, increased control comes at a cost; private registries require infrastructure, maintenance, and operational oversight. They also place greater responsibility on internal teams to ensure that images are properly validated and secured.
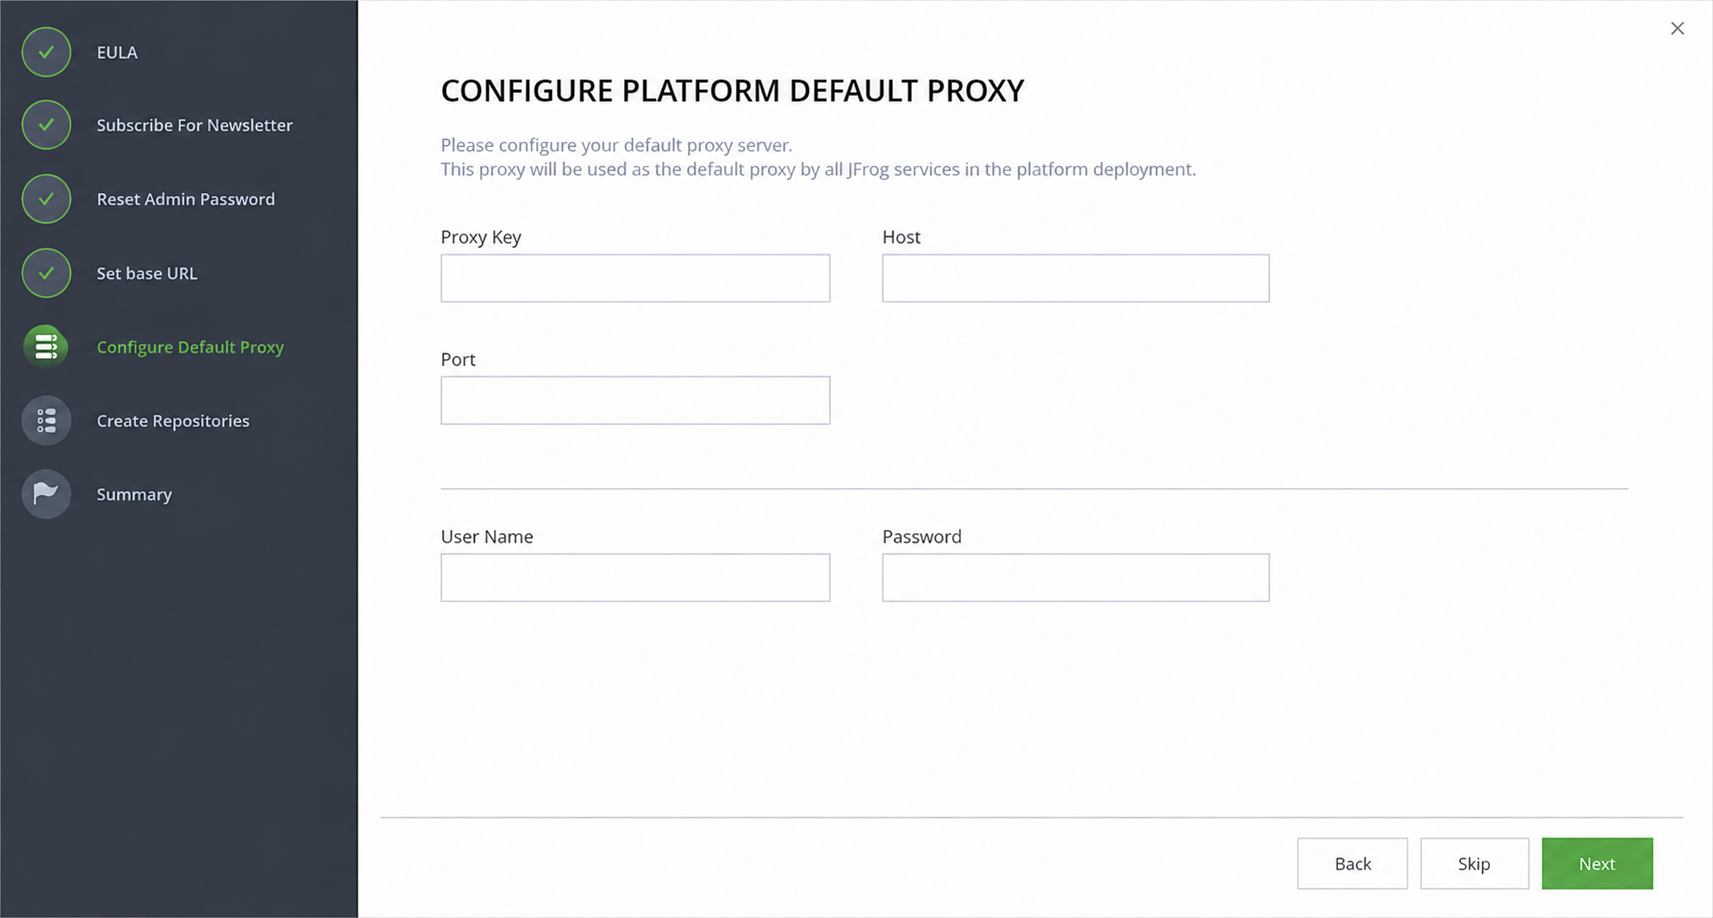
Source: JFrog Container Registry Onboarding
Security Through Visibility and Control
One of the most significant advantages of a private Docker registry is visibility. Organizations gain a clear understanding of what’s inside each image, how it was built, and who’s responsible for maintaining it. This transparency is critical for effective security management.
With this level of control, teams can implement practices such as:
- Image signing and verification
- Vulnerability scanning before deployment
- Enforcement of minimal base images
- Continuous monitoring of dependencies
These measures are difficult to enforce consistently in a public registry environment, where visibility is limited and control is distributed. That said, visibility alone is not enough. It must be paired with disciplined processes and tooling to ensure the consistent application of security policies across organizations.
The False Sense of Security in Isolation
Although private registries offer clear advantages, they aren’t inherently secure. In fact, they can create a false sense of security if not properly managed.
A private container registry is only as secure as the practices surrounding it. If teams continue to pull unverified images from external sources and push them into their private environment without validation, the risk remains unchanged.
Similarly, if vulnerability scanning and runtime protections aren’t integrated into the workflow, private registries can become repositories of outdated or insecure images.
Balancing Speed and Security
The decision between public and private registries often comes down to a balance between speed and security. Public registries like Docker Hub enable rapid development by providing instant access to a wide range of images. Private registries emphasize control and governance at the expense of agility.
For many organizations, the optimal approach isn’t one or the other but a hybrid model. In hybrid models:
- Public registries serve as a source of base images.
- Images are validated, scanned, and hardened internally.
- A private container registry stores and distributes approved images.
This approach allows teams to benefit from the breadth of public ecosystems while maintaining control over what ultimately enters production.
The Role of Policy and Automation
Regardless of the registry strategy, effective security depends on consistent enforcement. Manual processes are prone to error, and they don’t scale well in dynamic environments.
Automation plays a critical role in bridging this gap. By embedding security policies throughout the software development lifecycle, organizations can ensure that only compliant images are allowed to progress through the deployment process.
Examples of automated controls include:
- Blocking images with known vulnerabilities
- Enforcing the use of approved base images
- Verifying image signatures before deployment
- Preventing the use of “latest” tags in production
These controls standardize security practices across teams and reduce reliance on individual judgment.
Source: Alonchik_73/Shutterstock.com
A Shifting Threat Landscape
As container adoption continues to grow, so does the sophistication of attacks that target container ecosystems. Aware that compromising a single image can have far-reaching consequences, threat actors are increasingly focusing on software supply chain vulnerabilities.
This trend reinforces the importance of registry security. Whether using Docker Hub or a private Docker registry, organizations must assume that threats can originate at any point in the pipeline. Proactive measures, such as continuous scanning, runtime monitoring, and strict access controls, are essential for staying ahead of evolving risks.
Choosing With Intent
The choice between Docker Hub and private registries is a reflection of an organization’s security posture and risk tolerance. Public registries offer unmatched convenience and access, but they require careful scrutiny and validation. Private registries provide control and visibility, but demand disciplined management and investment.
Ultimately, the most effective strategy is one that combines the strengths of both approaches while mitigating their weaknesses. By treating the container registry as a critical component of the software supply chain, organizations can build a more resilient and secure foundation for modern application delivery.
Enjoyed this article? Sign up for our newsletter to receive regular insights and stay connected.