
Your curated roundup from genesis-aka.net / IT Professional · 32 articles this week
AI Coding Agents & the Developer Workflow
‘I can’t stop’: 80% of developers find AI coding more addictive than helpful (August 26)
AI coding assistants speed up code generation but create verification debt, larger reviews and more operational risk. For IT teams the real challenge is redesigning delivery controls, testing and governance so AI-driven output does not erode maintainability or developer sustainability.
AI Agents Are Writing Code Faster Than Anyone Can Review It. Tessl Is Betting On Standards To Close That Gap (August 26)
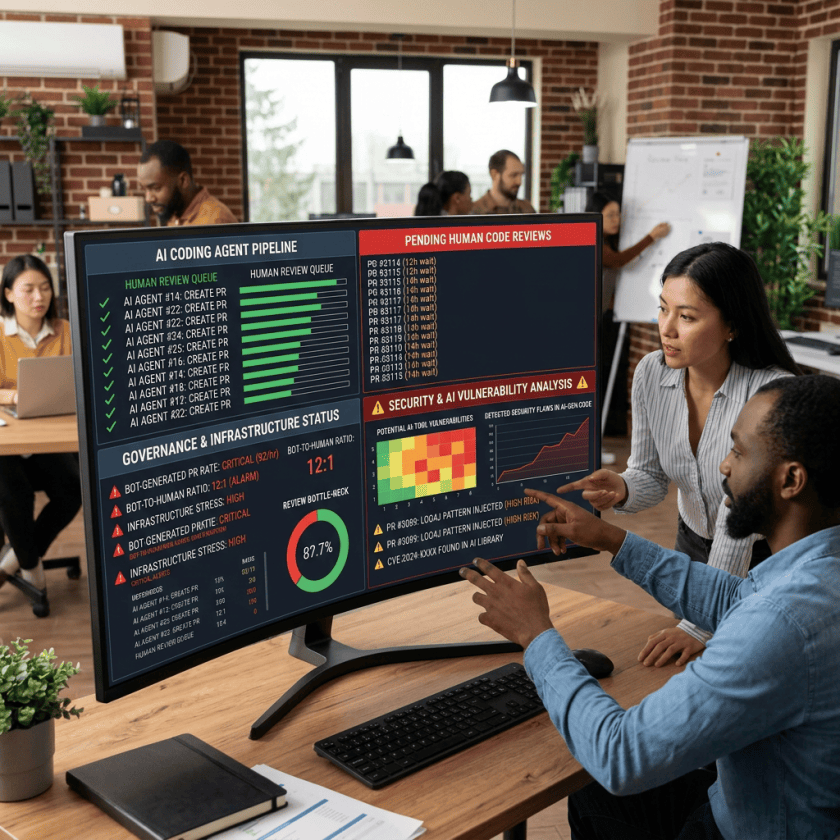
As coding agents flood teams with pull requests, the bottleneck shifts from writing code to reviewing it. Tessl’s answer is to turn review standards into versioned, portable controls that scale inside CI/CD — making governance, review latency and policy lock-in the decisive questions rather than tool choice.
Cursor launches Origin code hosting service to compete with GitHub (August 26)
Cursor’s Origin is notable not just as a Git hosting service but as a potential control plane for AI-assisted development. IT teams should focus on governance, sync authority, secrets handling and observability as code hosting, agents and deployment workflows converge.
Warp’s new system is an out-of-the-box software factory for AI development (August 25)
Warp’s software-factory approach raises the harder question of how to operationalize coding agents with governance, observability, evaluation and cost control. The opportunity is faster adoption; the risk is locking core SDLC workflows into a new orchestration layer before controls and review paths mature.
Are LLMs Equally Good (or Bad) at Building Secure Software? (August 25)
Benchmark wins matter less than governing model choice by framework, security risk and total delivery cost. AI code generation needs pipeline controls, outcome-based cost tracking and regular re-evaluation as models evolve.
Deterministic Robots, Agentic Reasoning: Balancing Reliability and Flexibility in Software Test Automation (August 26)
The choice is not robots versus agents but where each belongs in delivery and operations. The value lies in separating deterministic release controls from AI-assisted exploration while managing cost, auditability and operational confidence.
Agent Platforms, Runtimes & Governance
Red Hat Readies an MCP Server to Help LLMs Manage Kubernetes (August 26)
Red Hat’s Kubernetes MCP server introduces a new AI-to-cluster control path, raising practical questions about trust boundaries, RBAC scope, auditability and deployment model. The opportunity is faster operations; the challenge is governing LLM-driven infrastructure access like any other production interface.
Block’s open-source Berd matters less as a chatbot wrapper than as a potential control layer for enterprise agent workflows. Its local-first, multi-harness design could reduce model lock-in, but it pushes governance, endpoint security, provider routing and lifecycle management squarely onto IT teams.
TrueForge raises a bigger enterprise question than benchmark cost: whether agent runtimes can be made vendor-neutral without losing governance. Examine the hidden trade-offs around identity, policy enforcement, persistence, sandboxing and operational resilience before treating lower token spend as the deciding factor.
What the Microservices Era Can Teach Us About AI (August 26)
Agentic AI needs more than microservices-era patterns. The real challenge is building runtimes that preserve state, enforce per-step identity and expose auditable decision trails across long-running workflows without locking the platform to one cloud, model or framework.
Production-Grade AI Eval Systems. What I Learned Putting LLMs on Call (August 24)
Production AI needs more than uptime dashboards. Eval pipelines, sampled trace analysis, pinned model and retrieval changes, and cross-team incident runbooks are becoming core operational controls for LLM systems that fail silently while infrastructure metrics stay green.
Platform Resilience & CI/CD
GitHub Actions Hit Three-Nines Failure; One August Outage Consumed Year’s Downtime Budget (August 26)
A single August outage burned through the year’s entire downtime budget for GitHub Actions. The lesson is resilience: separating source control, build execution, identity and artifact delivery so one vendor failure domain does not halt releases, integrations and recovery operations at once.
Microsoft’s GitHub Hit by Major Outage as AI-Driven Demand Strains Infrastructure (August 25)
GitHub’s outage highlights how tightly coupled source control, CI/CD and AI tooling have become. The real issue is architectural concentration, and whether engineering organisations can keep building, releasing and responding when a shared platform fails.
Apple Silicon and Xcode 27 images available in pay-as-you-go (preview) (August 24)
Azure Pipelines’ new Apple Silicon runners are a CI architecture change more than a feature checkbox. Teams must revalidate arm64 dependencies, govern Xcode-specific images carefully, and reassess pipeline cost efficiency under per-minute billing instead of parallelism-based pricing.
Security & Software Supply Chain
Docker Hub vs. Private Registries: Security Tradeoffs (August 26)
Container registry strategy is really a software supply chain design choice. The key issue is where trust, validation and policy enforcement happen as images move from public sources into internal CI/CD pipelines and production platforms.
How Base Images Impact Software Supply Chain Security in Kubernetes (August 24)
Base-image security becomes meaningful only when enforced through platform policy, signed artifacts, automated rebuilds and runtime controls. The key issue is less image selection than an operational model that limits drift, shortens patch latency and preserves incident response capability.
Why Cryptographic Inventory Is the First Step Toward Quantum Readiness (August 26)
Quantum readiness is less about choosing new algorithms than building continuous visibility into where cryptography lives across pipelines, containers, Kubernetes and third-party services. The real work is linking crypto dependencies to ownership, architecture and operational change paths.
Microsoft Copilot reveals secret input that allowed it to be hacked (August 25)
The Copilot flaw shows how deep links, prefilled prompts and undocumented parameters can turn usability features into execution paths. IT teams should review assistant integrations as attack surfaces, not just model behavior, and enforce guardrails in client and service architecture.
Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat (August 25)
The isolated-vm flaw is a reminder that secure code execution depends on more than the sandbox primitive itself. For teams running user- or AI-generated JavaScript, the risk lies in host-guest bindings, serialization paths and whether process-level isolation exists beyond the Node.js runtime.
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript (August 24)
GitHub’s CodeQL update matters less for raw query count than for pipeline security signal quality. Focus on how improved GitHub Actions and modern JavaScript modeling affect triage workflows, baseline shifts and custom controls built around self-hosted runner assumptions.
Teleport puts developer Linux desktops under production access controls (August 26)
Teleport’s Linux desktop support extends production-style identity controls to the machines developers actually use. The opportunity is tighter auditability and reduced credential sprawl, but success depends on integrating those controls without disrupting Linux-based engineering workflows.
Coders Say They Already Found Workarounds to Claude’s Invisible Watermarks (August 25)
Watermark workarounds highlight a broader problem: text-based AI provenance is fragile once content moves through editing, translation or other LLM pipelines. Enterprises should treat watermark detection as a weak signal and rely on layered telemetry, policy and lifecycle metadata instead.
Cloud, Data & Infrastructure
Consistency is the new latency: AI at the data layer (August 26)
As AI agents move from answering questions to taking actions, data consistency becomes an application-level reliability requirement. Teams need explicit freshness guarantees, observability for stale-context failures, and architecture patterns matching storage semantics to each workflow’s operational risk.
AWS Glue 6.0 now available with 30% lower price and full Apache Iceberg v3 support (August 25)
AWS Glue 6.0 is more than a 30% price cut: Iceberg v3 support and the Spark 4.1 runtime could reshape semi-structured data pipelines, PySpark performance and low-latency streaming. The open questions are stack compatibility, migration risk and whether downstream tools handle the newer table semantics.
Layered data architecture turns enterprise data into a system of intelligence (August 25)
Knowledge graphs matter less as standalone technology than as a semantic control layer for AI-native data stacks. The challenge is integrating lineage, entity resolution and policy metadata so agents can produce explainable answers without breaking governance or trust.
The AI inference race moves beyond GPUs to reshape data center infrastructure (August 25)
Inference performance is becoming a full-stack issue, with storage, network contention and data locality shaping token delivery as much as GPUs do. The challenge is architecting memory, retrieval and governed data access for predictable performance at scale.
Best Strategies for Cloud Native Cost Optimization (August 25)
Cloud-native cost control is not a billing exercise; it is shaped by architecture, scaling signals and CI/CD policy. The question is how to embed cost accountability into platform engineering, deployment workflows and workload design before waste becomes normal operations.
CNCF Graduates Kubeflow for Production AI on Kubernetes (August 25)
Kubeflow’s CNCF graduation signals that Kubernetes is maturing into a serious control plane for production AI. The real issue is not project status but how to standardize training, serving, governance and multi-tenant operations without replacing vendor lock-in with platform complexity.
What It Really Takes to Run OpenTelemetry (August 25)
OpenTelemetry removes vendor lock-in at the instrumentation layer, but running it at scale introduces collector, storage and correlation overhead teams underestimate. The decision is whether observability should be operated as internal platform infrastructure or consumed as a managed service.
AI Frontier & Research
DeepSeek debuts multimodal language model competitive with Opus 4.8 (August 24)
DeepSeek’s new multimodal model matters less as a benchmark story than as a deployment question. Assess API maturity, long-context performance, vision-pipeline bottlenecks and vendor dependency before treating strong multimodal scores as production readiness.
CLIP Image Encoder Fine-Tuning Hurts Cross-Domain AI Models, IJCAI Study Finds (August 25)
The IJCAI study challenges a common CLIP deployment habit: tuning the image encoder first. For teams shipping vision-language models into mixed real-world data streams, adapter placement, uncertainty gating and drift testing may matter more than task-local accuracy gains.
How Generalist uses human demonstration data for robot learning (August 25)
Generalist’s approach points to a shift in industrial automation: robot learning becomes a data, integration and operations problem. The challenge is not just model capability but safe deployment, interoperability, observability and lifecycle control across mixed robot environments.
Editor’s Takeaway
This week’s dominant theme is the collision between AI-accelerated code production and the delivery infrastructure that has to absorb it. Agents are generating pull requests faster than humans can review them — Tessl is betting on portable review standards, Warp on a packaged software factory, and Cursor on owning the code-hosting control plane — while 80% of developers describe AI coding as more addictive than helpful. At the same time, the platforms carrying that load are visibly strained: GitHub Actions burned an entire year’s downtime budget in a single August outage, and a second GitHub incident the same week exposed how much of modern software delivery now sits inside one failure domain. The security stories rhyme with this — Copilot’s prefilled-prompt flaw, the isolated-vm sandbox escape, and fragile AI watermarking all show that AI features become attack surface faster than governance catches up. The practical takeaway for IT professionals is to stop treating AI tooling as a productivity add-on and start treating it as production infrastructure: give it identity, policy, eval pipelines, cryptographic inventory and a blast-radius plan, and architect deliberately against concentration risk in the platforms it depends on.
Explore the full IT Professional archive at genesis-aka.net/information-technology/professional/
Enjoyed this article? Sign up for our newsletter to receive regular insights and stay connected.