Your curated roundup from genesis-aka.net / IT Professional · 23 articles this week
AI Agents & Governance
Atlassian Aims to Fill Context and Governance Gap for AI Coding Agents (September 16)
Atlassian’s update points to a bigger SDLC change: AI agents need structured context, scoped permissions and auditable workflows before they can operate safely at scale. The real challenge for IT teams is turning project systems such as Jira and Confluence into a reliable control plane for multi-agent software delivery.
AI Agent Guardrails Are Not Enough: Enterprise Security Needs an Enforcement Layer (September 15)
AI agent security now depends less on better prompts and more on enforceable runtime controls. The real work for IT teams is building an action-level policy layer with strong identity, interception points and auditable decisions that persist across tools, frameworks and cloud environments.
AWS, Azure and Google Cloud: What’s Different About Their MCP Servers (September 15)
AWS, Azure and Google Cloud may all support the Model Context Protocol, but they expose very different trust boundaries. For IT teams, the real issue is how each server model changes identity, governance, auditability and blast radius when agents touch infrastructure or enterprise data.
GitHub Puts Guardrails on Copilot’s Sandbox Inside JetBrains IDEs (September 16)
GitHub’s new Copilot sandbox controls for JetBrains matter less as a plugin feature than as a governance layer for AI agents executing inside enterprise developer environments. IT teams now need to treat IDE-based assistants like managed runtime surfaces with verifiable policy, least-privilege boundaries and operational oversight.
Why AI Agents Shouldn’t Guess at Vulnerability Exploitability (September 14)
AI agents can speed vulnerability triage, but only if exploitability decisions are grounded in joined supply-chain and runtime evidence. The real work is building deterministic, auditable graph-based analysis that models dependencies, reachability and deployment context before AI explains the result.
AI in the Developer Workflow
GitHub’s New Copilot Feature Takes the Guesswork Out of Picking AI Models (September 16)
GitHub’s HydraFusion points to a broader shift: AI coding tools are becoming orchestration layers, not single-model assistants. For IT teams, the real issue is policy, auditability and telemetry — how model routing, cost control and code provenance are governed as multi-model workflows enter production.
AI Has Turned Verification Into the New DevOps Bottleneck (September 15)
AI coding gains create a downstream delivery problem: verification, release evidence and behavioral testing are not scaling at the same pace. The real challenge is redesigning CI/CD to evaluate AI-linked changes with distinct gates, telemetry and rollback strategies.
Test Creation Was Never the Bottleneck (September 15)
AI-assisted coding is accelerating output, but many teams have not redesigned review, traceability and release controls to match. The question for IT leaders is whether architecture, pipeline policy and operational evidence can scale verification without turning every productivity gain into more delivery risk.
Trustworthy AI Won’t Scale Without A New Quality Playbook: Forrester Offers One (September 16)
For AI-enabled apps, Forrester argues quality engineering now has to cover probabilistic behavior, retrieval, prompts and agent actions — not just code correctness. The real challenge is integrating evals, telemetry, governance and release gates into one operational quality system.
Kubernetes & Platform Engineering
Kubernetes Did Not Miss the AI Wave. It Absorbed It (September 14)
Kubernetes may be the common runtime for AI inference, but enterprise portability and operability now hinge on higher-layer choices such as gateways, observability, orchestration and fallback policy. The real challenge is defining which AI control points stay standard and which introduce lock-in.
Manifestly Safer, Why Kubernetes Wants Developers to Speak KYAML (September 15)
KYAML’s value is operational, not cosmetic: it can make Kubernetes manifests more deterministic across Helm, CI and GitOps workflows. The key question is where to enforce stricter configuration rules so syntax safety improves reviews, policy checks and deployment reliability.
K8sGPT and the Guardrails for AI-Assisted Kubernetes Troubleshooting (September 15)
AI-assisted Kubernetes triage is most valuable when treated as a controlled operational interface, not a free-form cluster agent. For platform teams, the real work is designing RBAC, data-governance, auditability and GitOps-based remediation boundaries so explanations accelerate troubleshooting without weakening production control.
Jenkins + OpenChoreo: Adopt a modern Internal Developer Platform (IDP) Without Replacing Your CI System (September 15)
This Jenkins-to-IDP pattern matters less for its API call than for its operating-model shift: separating build from deployment governance. Teams should focus on artifact identity, cross-system auditability, shared-library standardization and credential boundaries before scaling the approach across hundreds of pipelines.
Cloud & Data Infrastructure
Introducing Amazon EBS Volume Clones across AWS accounts (September 16)
AWS cross-account EBS clones can streamline multi-account environment refreshes, but IT teams should focus on AZ mapping, KMS key governance and RAM sharing controls first. Post-copy data-handling policy matters before the feature becomes a routine Dev/Test or recovery mechanism.
Two zones or three? A design framework for zone-resilient Azure workloads (September 15)
Azure zone resilience is really a component-level architecture decision, not a blanket three-zone rule. The key work is mapping dependencies, validating quorum and failover behavior, and proving post-failure capacity and latency under realistic operational tests.
Build declarative ETL pipelines with AWS Glue 6.0 (September 15)
AWS Glue 6.0’s declarative pipelines can reduce orchestration overhead, but the bigger question is how teams handle failure domains, recompute cost and incremental design. Production lifecycle control gets harder once multiple ETL stages collapse into a single managed execution model.
Accelerating Spark queries with Iceberg materialized views (September 14)
Apache Iceberg materialized views can hide Spark query acceleration behind the optimizer, but the real challenge is MV lifecycle design. That means choosing reusable versus exact-match views, controlling refresh and cache behavior, and proving rewrite reliability in production.
Security & Resilience
Q-Day is approaching. Most organizations aren’t ready (September 15)
Post-quantum migration is not just a security upgrade but a cross-stack architecture problem spanning PKI, identity, gateways, cloud services and software signing. IT teams need crypto-agility, dependency mapping and prioritized control-point upgrades before compressed timelines turn remediation into operational risk.
JFrog Artifactory Hacked in 24-Day Campaign; Rust Backdoors Survive Patching (September 14)
This incident is bigger than a vulnerable server: a compromised self-hosted Artifactory can undermine trusted build pipelines, tokens, plugins and downstream artifacts. Recovery requires integrity validation, secret rotation and supply-chain scoping — not just patching the platform.
GitHub’s August Outages Show Growth Is Outpacing Infrastructure (September 16)
GitHub’s outage pattern matters because Actions and Copilot now sit in many teams’ delivery path. The real issue for IT leaders is dependency concentration: fallback CI/CD paths, independent status checks and clearer separation of source-control, automation and AI-provider risk domains.
AI Infrastructure & Models
EMIB vs. CoWoS: Google, Amazon Back Intel for Inference as Nvidia Keeps Training on TSMC (September 16)
AI chip packaging is becoming an architectural decision, not a back-end manufacturing detail. For IT leaders, the EMIB-versus-CoWoS split affects accelerator strategy, software-stack portability, supply resilience and the operability of future training and inference platforms.
DeepSeek releases V4.1-Flash, says it outperforms flagship V4-Pro (September 15)
DeepSeek’s new model matters less for the benchmark claim than for what it implies operationally: cheaper inference, smaller cache footprints and automatic endpoint substitution. All three affect architecture, testing, observability and governance for teams building production AI services.
Extreme Networks’ Agent ONE Coworker moves AI networking from dashboards to answers (September 15)
Extreme Networks’ AI push matters less for the chatbot and more for the operating model behind it: normalized cross-domain context, ambient incident nudges and human-governed automation. The real test is integration with telemetry, runbooks and service-management workflows — not demo-friendly answers alone.
Editor’s Takeaway
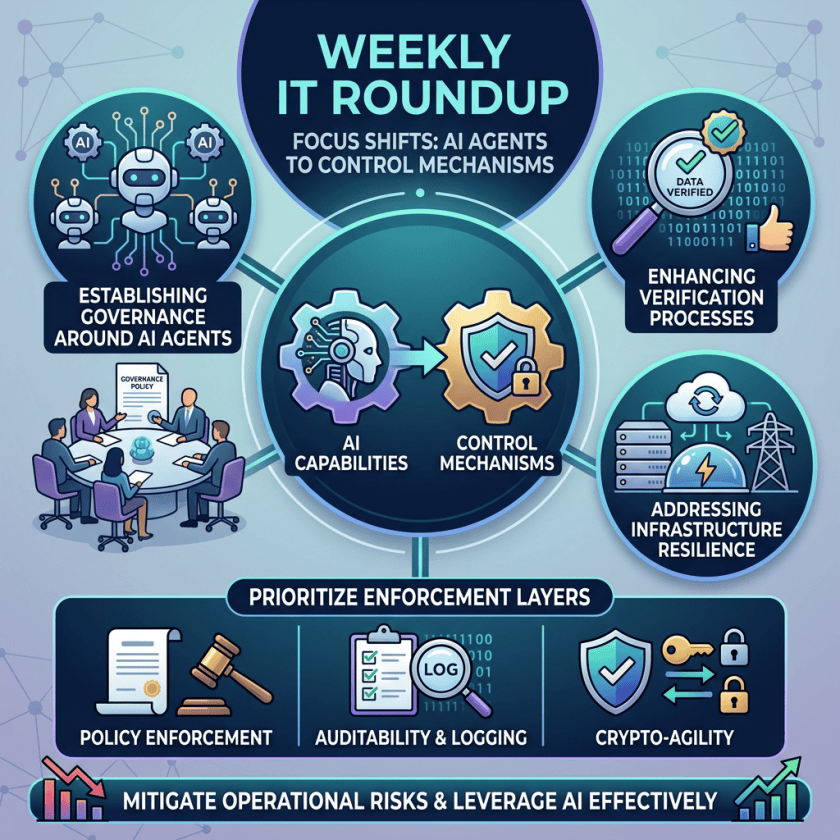
The through-line across all 23 articles this week is that AI has stopped being a capability question and become a control question. Whether the subject was GitHub sandboxing Copilot inside JetBrains, Atlassian turning project systems into an agent control plane, the three hyperscalers exposing very different MCP trust boundaries, or K8sGPT triaging clusters, the recurring conclusion was the same: the interesting engineering work now sits in identity, scoped permissions, auditability and blast-radius containment rather than in the model itself. That pressure shows up downstream too — two separate pieces argued that verification, not code generation, is the new delivery bottleneck, and Forrester’s quality playbook makes the same case for probabilistic systems. Meanwhile the infrastructure stories (Azure zone design, Glue 6.0, Iceberg materialized views, EMIB versus CoWoS packaging) and the security stories (Q-Day readiness, the 24-day Artifactory compromise, GitHub’s outage concentration) all reinforce that the foundations carrying these agents are themselves being re-architected. For IT professionals, the practical takeaway is to invest this quarter in the enforcement layer — policy, evidence, rollback and crypto-agility — because that is what determines whether AI-era velocity turns into operational risk or operational leverage.
Explore the full IT Professional archive at genesis-aka.net/information-technology/professional/
For regular updates, please subscribe our newsletter https://genesis-aka.net/newsletter/
Enjoyed this article? Sign up for our newsletter to receive regular insights and stay connected.